
In the topology above, NSX edge load balancer is deployed in
one arm mode.
NSX edge load balancer has a single layer 3 interface which
is connected to Distributed Logical Router via a logical switch.
This logical switch is dedicated for Load Balancing Tier.
There is also a Web Tier hosting web servers and these web
servers are connected to Distributed Logical Router via Web Tier logical
switch.
Pool members corresponding to the virtual server are both residing
on this Web Tier Logical switch.
The routing topology of this whole setup has already been
covered in this post here.
The single vnic of NSX Edge Load Balancer has primary IP
address as 172.16.20.100 / 24
The single vnic of NSX Edge Load Balancer also has secondary
IP addresses assigned to it as below
Secondary IP 1 – 172.16.20.101
Secondary IP 2 – 172.16.20.102
We will be using one of these secondary IP addresses to create
a virtual server.
=========================================
Configuration:
We will first enable the load balancer service on NSX Edge Services Gateway.
 |
| Enable Load Balancer Service |
 |
| Application Profile |
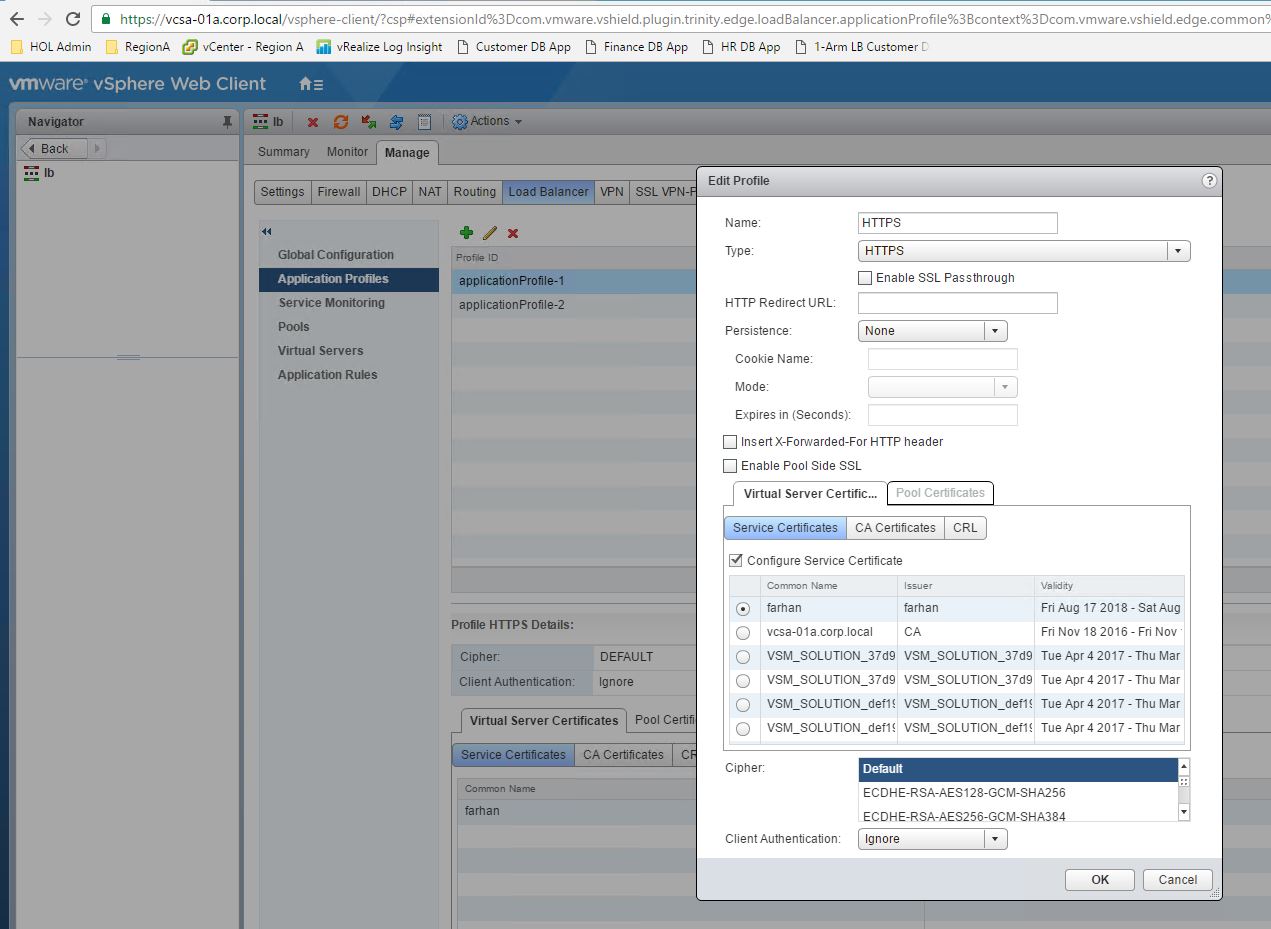
Application profile is created then and the details are as
below
Application profile name - HTTPS
Application profile type – HTTPS
Certificate – For this lab setup, we have used a self-signed
certificate.
 |
| Server Pool |
Server pool is created as below
Pool name – pool
Algorithm – Round robin
Members – Virtual Machine web-01a, tcp/80
 |
| Virtual Server |
Virtual server is created using the secondary IP address and
the virtual server details are as below
Virtual Server IP – 172.16.20.101
Virtual Server port – 443
Application Profile – HTTPS
Server pool name – pool
====================================
A management station is residing on the physical network
with IP address as 192.168.110.10
We have also taken packet captures on the NSX Edge Load
Balancer interface for below communications
- Communication between the management station and the virtual server 172.16.20.101, tcp port 443
- Communication between NSX Edge Load Balancer and the pool members.

Comm. between Mgmt. Station & Virtual Server 
Comm. between load balancer & pool members


It is worth noting that in the case when a secondary IP address 172.16.20.101 is assigned to single vnic of NSX Edge Load Balancer & the secondary IP address is used to create virtual server, the load balancer uses the primary IP address 172.16.20.100 to establish a connection between itself and the pool members.
Both the above packet captures are done at the same time while trying to access the web page at https://172.16.20.101
NSX Edge Load Balancer is working as a reverse proxy and from the packet captures, it is evident that there are two different TCP connections -
- One between initiator and load balancer
- The other between load balancer and pool member
NSX Edge Load Balancer supports below features:
1. SSL Offload
2. SSL Bridging
3. HTTP Profile with ‘insert X-Forwarded-For’
4. Cookie based persistence as well as source IP based persistence is supported.
5. Redirection from http to https
6. Multiple ciphers can be used.
7. Load balancing algorithms which are supported are:
- Round robin
- IP Hash
- Least connection
- URI
- HTTPHEADER
- URL
Some very useful resources:
NSX Admin Guide
https://docs.vmware.com/en/VMware-NSX-for-vSphere/6.4/nsx_64_admin.pdf
NSX Reference Design Guide
https://www.vmware.com/content/dam/digitalmarketing/vmware/en/pdf/products/nsx/vmw-nsx-network-virtualization-design-guide.pdf

